Federal authorities moved Wednesday to dismantle a major Chinese state-sponsored cyber operation, executing court-authorized domain seizures that took down two hacking platforms used to target American critical infrastructure and government agencies.
According to court documents unsealed in the Southern District of California, the Justice Department and the FBI seized key internet domains used by a People’s Republic of China (PRC) group known as “QTFY.” Operating under the front of Nanjing Xinjiuwei Network Technology Company, the group allegedly built and ran two hacking tools called “QScan” and “QTRouter.”
Investigators said the group’s victims include major government institutions, such as the U.S. Senate, the Federal Reserve, NASA, the Department of Energy, the Department of Justice, the Department of Health and Human Services, and the National Institutes of Health.
Commercial targets included power companies, hospitals, defense contractors, and telecommunications providers.
“State-sponsored malicious hackers preying on America’s critical infrastructure will be stopped and prosecuted. We are here to ensure security for the American people and will use every tool we have to keep that promise,” Attorney General Todd Blanche said in a statement. “Federal law enforcement investigated and disabled the PRC’s malicious software, the latest in a series of technical operations to dismantle indiscriminate hacking activities sponsored by the People’s Republic of China.”
Federal filings outline how QTFY sold hacking capabilities to clients that included China’s Ministry of State Security and the People’s Liberation Army. The group’s tools functioned as an automated pipeline: QScan scanned the internet for software flaws and infected thousands of internet-connected devices worldwide, including smart appliances and routers. Those compromised devices were then funneled into QTRouter, an obfuscation network that routed cyberattacks through local devices to disguise the Chinese origin of the intrusions.
Because the seized web addresses—qtproxy.xyz, qt-proxy.org, and qt-team.com—were hard-coded into the malware for essential functions like communication and authentication, taking control of the domains effectively rendered both platforms inoperable.
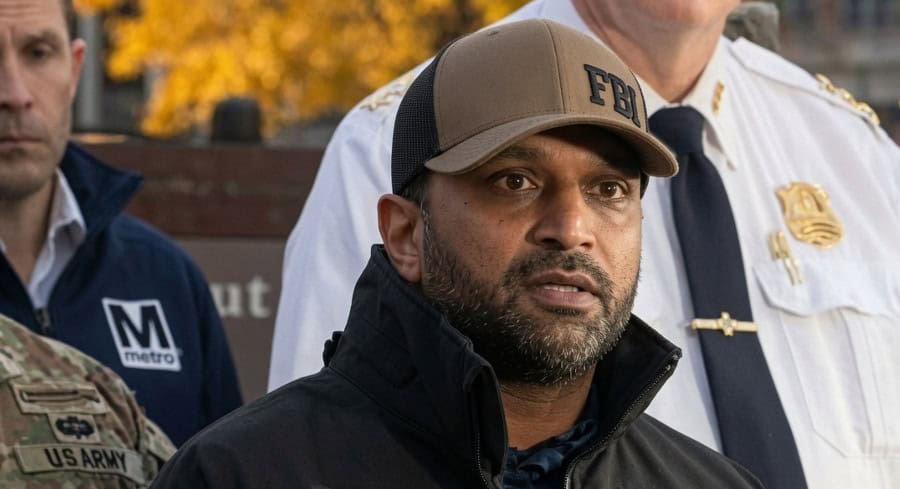
“Today we announced the disruption of a global botnet and hacking platform used by Chinese state-sponsored hackers to target U.S. critical infrastructure,” FBI Director Kash Patel said. “These tools were used by PRC cyber actors to hide the origin of their attacks. Thanks to the work of FBI San Diego, FBI Cyber Division, and DOJ partners, we seized adversary infrastructure and shut these platforms down.”
Court records trace QTFY activity back to at least 2018. The group carried out extensive cyber operations, including an attempted intrusion at NASA in 2019, attacks against three Department of Energy national laboratories in September 2024, and the theft of configuration files and user credentials from more than 300 U.S. organizations earlier that year.
“Today’s announcement demonstrates the Justice Department’s steadfast commitment to going on the offensive against cyber threats to the national security,” said Assistant Attorney General for National Security John A. Eisenberg. “These court-authorized seizures deny PRC-linked hackers access to tools they use to mount online attacks against our Nation’s critical infrastructure.”
The action is the latest in a series of federal operations against Chinese hacking infrastructure. In 2025, the FBI removed PlugX malware tied to the Mustang Panda hacking collective from more than 4,000 U.S. systems, following earlier disruptions of botnets operated by groups known as Flax Typhoon and Volt Typhoon.
“We’re taking the fight to PRC-sponsored cybercriminals to protect the critical services Americans rely on every day,” said U.S. Attorney Adam Gordon for the Southern District of California.
The operation was carried out jointly by the FBI’s San Diego Field Office, the FBI Cyber Division, the U.S. Attorney’s Office for the Southern District of California, and the National Security Cyber Section of the Department of Justice. Alongside the seizures, the FBI and the National Security Agency issued a joint technical advisory detailing indicators of compromise tied to QTFY systems.
READ: ‘Chucky’ Caught In Vegas: Masked Suspect Arrested After Flight From Pennsylvania
Please make a small donation to the Tampa Free Press to help sustain independent journalism. Your contribution enables us to continue delivering high-quality, local, and national news coverage.
Sign up: Subscribe to our free newsletter for a curated selection of top stories delivered straight to your inbox.
